Conundrum provides your cybersecurity stakeholders with answers to their PIRs in near real-time, from ransomware campaigns to emerging vulnerabilities.
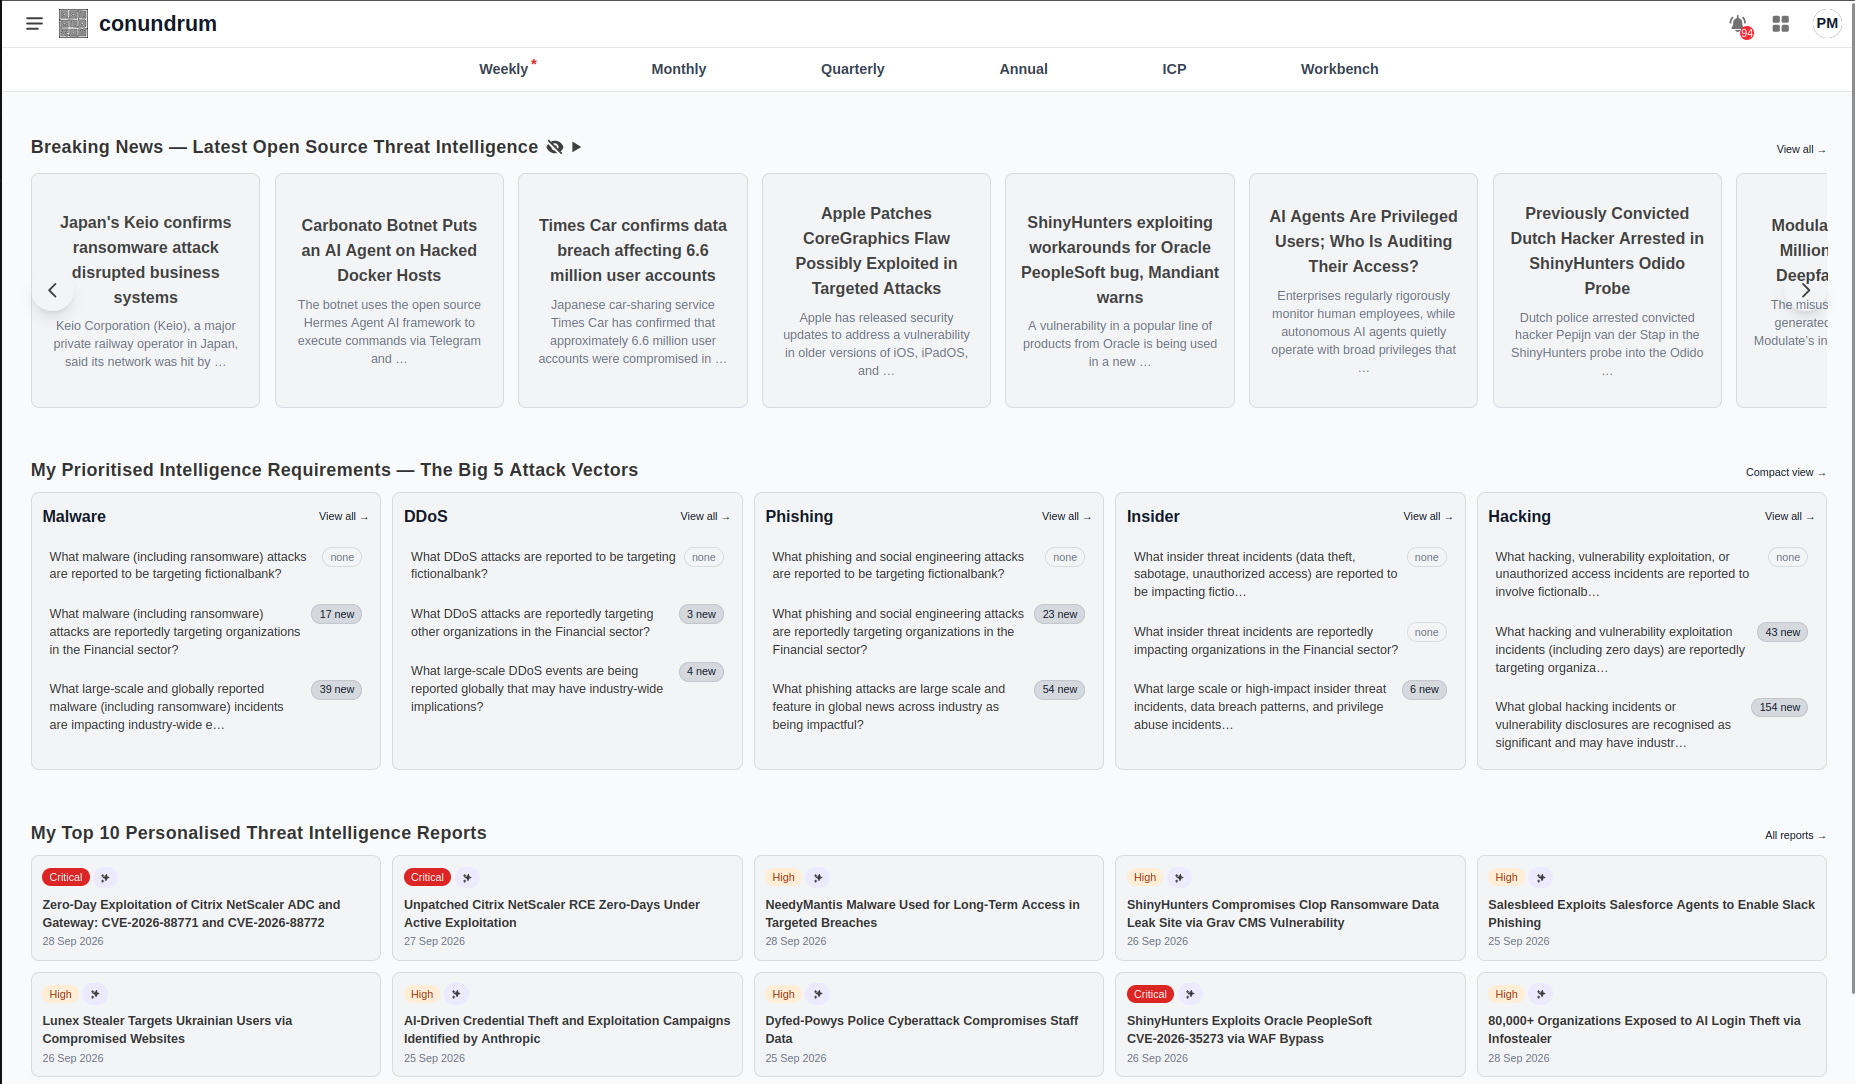
Traditional CTI platforms are expensive, complex, and require extensive configuration. Conundrum is built to answer your requirements from the day it is switched on.
Collected intelligence becomes finished reporting (situation, assessment and recommendations) rather than another queue to triage.
Operates independently of your client systems: no network access to your infrastructure, and no document upload required.
Automate collection, analysis and dissemination while your analysts stay in control of what gets said.
50+ OSINT sources, collected around the clock, with a configurable collection plan and automatic PIR mapping.
Source-checked reporting with entity extraction, IOC capture and mapping to the frameworks your analysts already use.
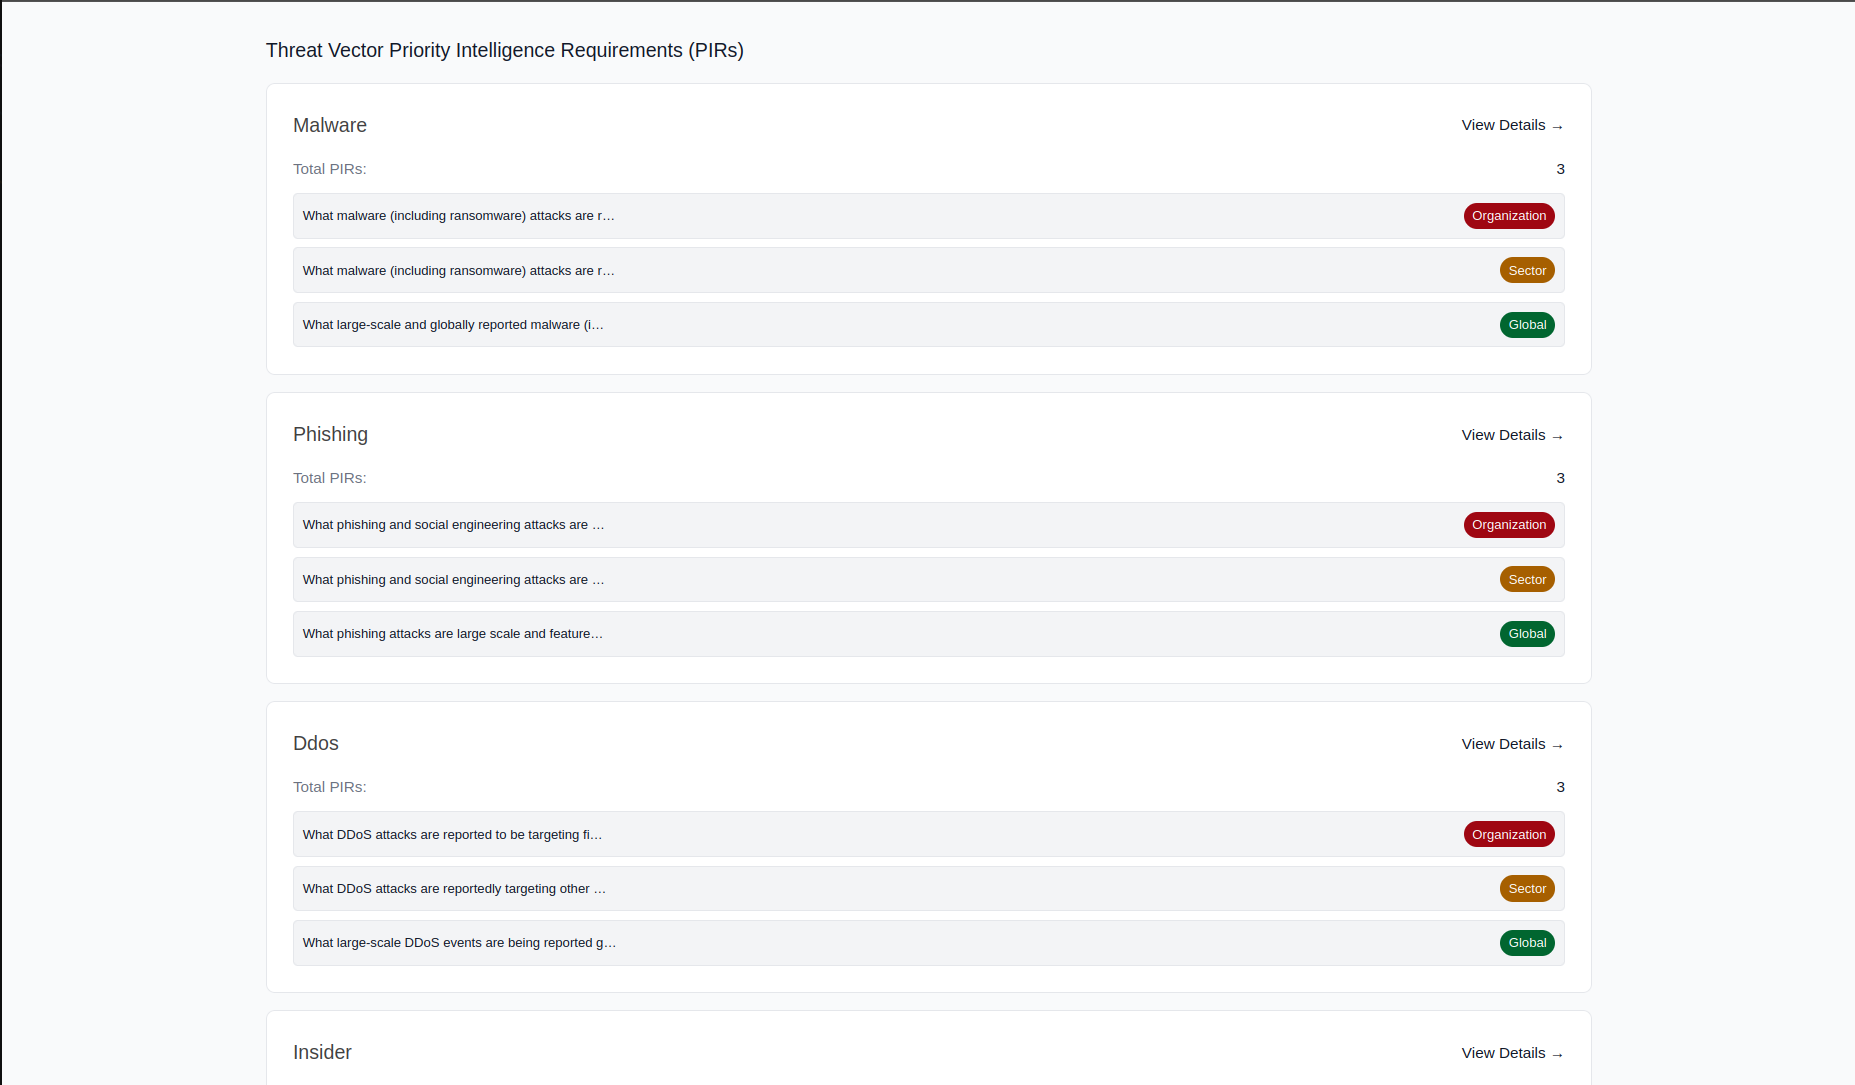
Tweak your collection plans and tailor your PIRs to the questions your own stakeholders are asking.
Schema-level separation ensures your intelligence data never mixes with another organisation's.
The intelligence cycle is a resource-intensive spiral. Conundrum automates the process so finished intelligence arrives timely and accurate.
Automated collection from 50+ sources, gathering threat feeds continuously at no per-item cost.
Collected intelligence is scored against your requirements, entities are extracted and resolved, and relevance is ranked per tier.
Reports are generated and checked against their own sources before publication, and unsupported assertions are held for review.
Finished intelligence routes to the people who need it, and the systems they work in, on rules you set.
A demo runs on your sector's intelligence, not a canned dataset.